XML-RPC Endpoints Enabling Secure Desktop Connections for Football Prediction Administration
Written by Petra Müller · Oct 7, 2026
XML-RPC Endpoints Enabling Secure Desktop Connections for Football Prediction Administration
Football prediction sites have expanded their reliance on structured data exchanges, and XML-RPC endpoints provide one established pathway for linking desktop applications directly to secure administrative interfaces. These endpoints operate through HTTP POST requests that carry XML-formatted method calls, allowing tools running on local machines to authenticate and perform actions such as content updates or odds adjustments without browser mediation. Observers note that this approach maintains compatibility with older desktop environments while supporting encrypted channels when configured with TLS certificates issued after standard validation procedures.
Core Mechanics of XML-RPC in Administrative Contexts
XML-RPC transmits structured requests that include method names and parameter arrays, then returns corresponding responses in the same format. On prediction platforms the method calls often target functions for batch uploading match forecasts or revising user access permissions, and the protocol's simplicity reduces the need for custom middleware layers. Researchers have documented that implementations typically require only a lightweight client library on the desktop side, which handles serialization and network transport while the server validates credentials against an internal directory service. Data from industry reports indicates that such setups appear in environments where teams manage multiple prediction models simultaneously and require consistent synchronization across distributed workstations.
Security Configurations for Admin Workflows
Secure deployment begins with restricting endpoint access to specific IP ranges or requiring mutual TLS authentication, measures that limit exposure to external scanning attempts. Administrators configure role-based permissions so that desktop-initiated calls execute only within predefined scopes, such as read-only queries for historical performance metrics or write access limited to designated categories of upcoming fixtures. According to cybersecurity guidelines published by the National Institute of Standards and Technology, logging every XML-RPC transaction with timestamp and originating identifier supports audit trails that meet compliance expectations in regulated markets. Those who maintain these systems often combine endpoint filtering with regular rotation of API keys stored in encrypted desktop vaults rather than plain configuration files.
What's notable is the way desktop tools leverage these connections to streamline repetitive tasks. A prediction analyst might draft detailed statistical breakdowns in a local spreadsheet application, then invoke an XML-RPC method that pushes the formatted content directly into the site's content management database. The transaction occurs over a single authenticated session, eliminating intermediate file uploads and reducing opportunities for transcription errors. Studies from academic computing departments have examined similar patterns in content-heavy sites and found measurable reductions in workflow latency when XML-RPC replaces manual browser-based entry sequences.
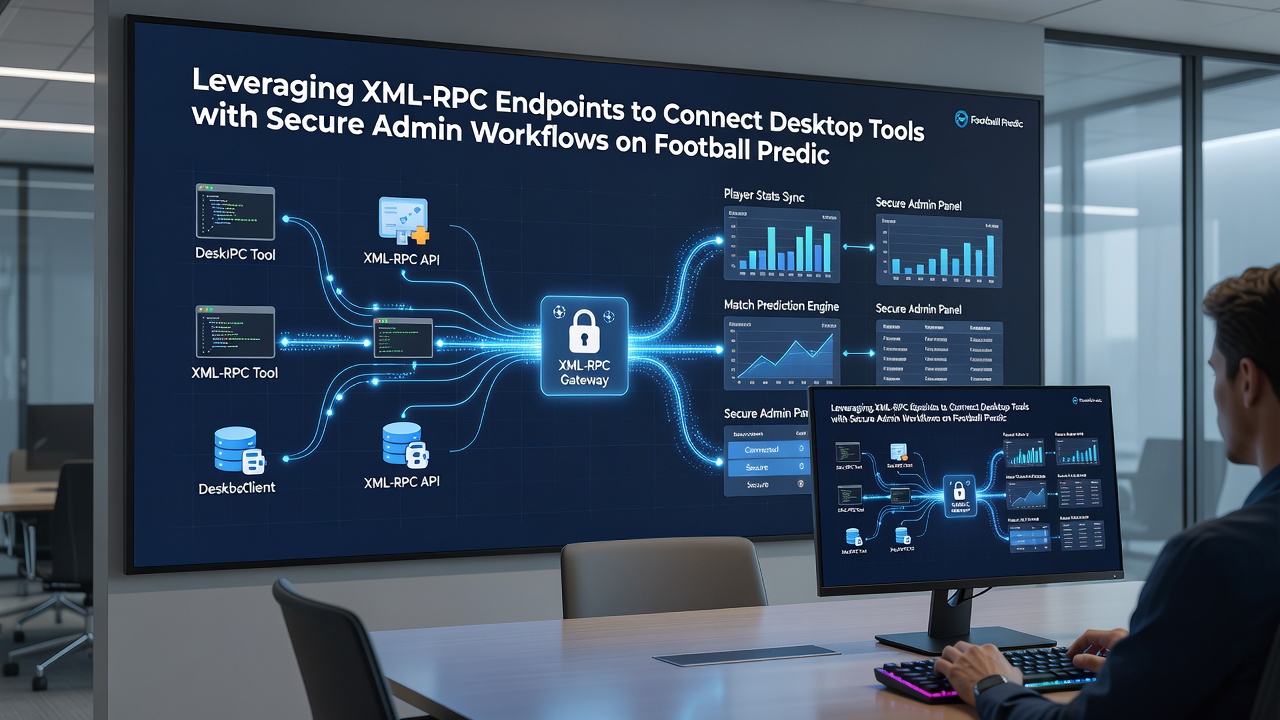
Integration Patterns Observed on Prediction Platforms
Many sites structure their XML-RPC interfaces around modular method groups that separate user management, content publication, and statistical data ingestion. Desktop utilities connect to these groups through configuration files that specify endpoint URLs and authentication tokens generated during initial setup. In October 2026 several European operators reported expanded use of such integrations following updates to data protection frameworks that emphasize encrypted administrative channels. The pattern allows teams located in different time zones to maintain synchronized prediction feeds while each contributor works within familiar desktop environments equipped with version-control extensions.
External monitoring tools can poll the same endpoints for health checks, confirming that response times remain within acceptable thresholds before large-scale match events. Trade associations tracking digital operations have recorded instances where sites using XML-RPC for desktop linkage experienced fewer interruptions during peak traffic periods compared with purely web-based admin sessions. This outcome stems from the protocol's lightweight payload size, which avoids the overhead associated with full-page rendering requests.
Practical Examples from Operational Deployments
One documented deployment involved a prediction platform serving multiple European leagues that equipped analysts with a custom desktop client built around an open-source XML-RPC library. The client authenticated via certificate-based credentials stored in a hardware security module, then executed methods that updated live odds tables and published pre-match analysis articles. System logs showed consistent daily volumes exceeding several thousand method calls without authentication failures after initial rollout. Another case centered on a North American operator that linked spreadsheet macros to XML-RPC endpoints for automated ingestion of model-generated forecasts, achieving direct database commits while preserving existing firewall rules that blocked general web admin access from external networks.
Considerations for Long-Term Maintenance
Platform operators routinely schedule endpoint version checks aligned with operating system updates on desktop machines to prevent serialization mismatches. Documentation maintained by development teams includes sample request payloads and expected response structures, which new staff members reference during onboarding. Figures from technology research groups reveal that organizations retaining XML-RPC alongside newer REST interfaces report sustained usage among legacy desktop tool users who prefer not to migrate to browser-centric workflows. Regular penetration testing exercises target these endpoints specifically, verifying that input validation routines reject malformed XML structures before they reach core application logic.
Additional safeguards include rate-limiting policies that throttle excessive calls from single desktop addresses and automated alerts triggered when authentication patterns deviate from established baselines. These measures align with broader recommendations issued by standards bodies focused on secure remote procedure mechanisms across industries.
Conclusion
XML-RPC endpoints continue to serve as a functional bridge between desktop applications and secure administrative systems on football prediction sites, delivering structured data exchange with defined security boundaries. Configurations that emphasize certificate validation, scoped permissions, and comprehensive logging support operational continuity while meeting external compliance expectations. As platforms evolve, the protocol's established specifications allow incremental enhancements without requiring wholesale replacement of existing desktop tooling ecosystems.